Decoding the Security Architecture of Modern Digital Wallets

The Evolution from Leather to Silicon
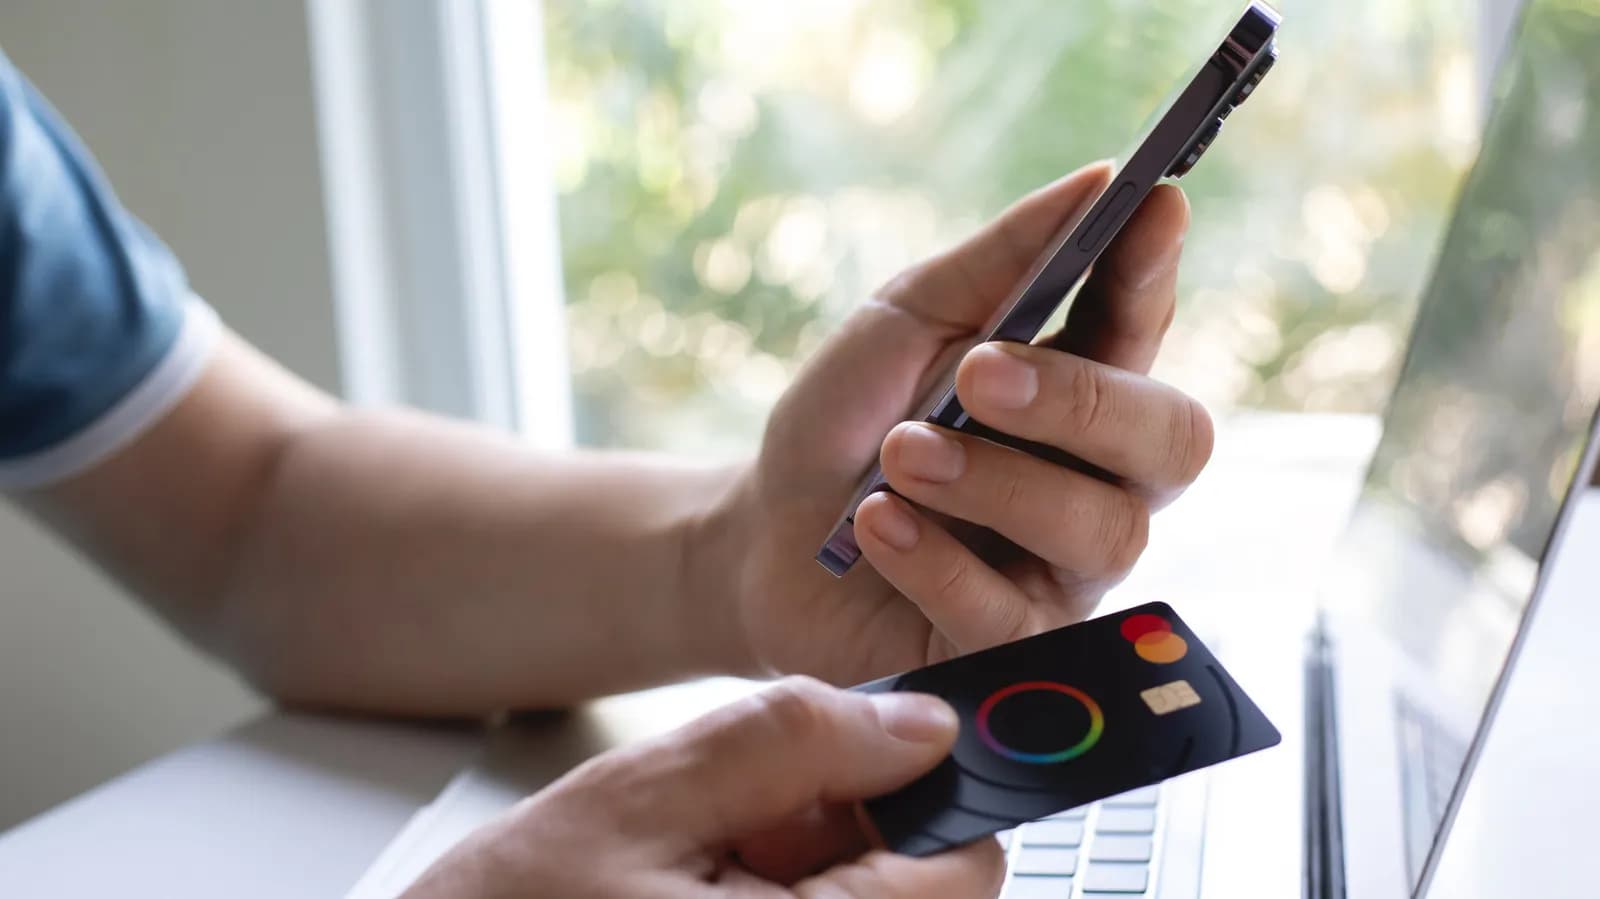
For generations, personal finance relied on physical infrastructure. Leather wallets, magnetic stripe cards, and signature lines formed the bedrock of daily commerce. While familiar, this analog paradigm carried inherent risks—lost cards, stolen numbers, and physical theft left consumers exposed. The rapid shift toward digital wallets marks a massive paradigm pivot, moving financial transactions away from vulnerable physical artifacts and into heavily encrypted, software-driven environments.
Today, platforms like Apple Wallet, Google Wallet, and specialized fintech applications have largely normalized contactless payments via smartphones and smartwatches. Beyond sheer convenience, these systems introduce a multi-layered security model that fundamentally transforms how payment credentials interact with merchant terminals. Rather than merely storing a digital image of a credit card, these applications deploy complex software and hardware protocols designed to mitigate fraud at scale.
Tokenization: Hiding Real Credentials
The core innovation powering digital wallet safety is tokenization. When a user adds a debit or credit card to their device, the actual Primary Account Number (PAN) is never stored locally on the hardware, nor is it transmitted to the merchant during a transaction. Instead, the payment network issues a unique digital token—a randomized string of numbers that maps back to the underlying account exclusively within secure server environments.
For developers and system architects, tokenization serves as a masterclass in reducing attack surfaces. If a merchant's point-of-sale terminal is compromised in a data breach, attackers only capture the transient token, which is useless outside of its specific context and token vault. This architecture decouples the merchant from raw financial data, dramatically lowering the risk profile for both consumers and businesses alike.
Hardware-Enforced Security and Biometrics
Software protocols alone cannot secure financial transactions without trusted hardware. Modern smartphones rely on dedicated security enclaves—isolated microprocessors embedded within the device's main chipset. These secure elements store sensitive cryptographic keys and execute sensitive operations completely isolated from the primary operating system, protecting them even if the main OS encounters a security flaw.
Furthermore, accessing and authorizing a payment requires active biometric verification. Unlike a physical card that anyone can swipe or tap if found on the ground, a digital wallet remains locked behind facial recognition, fingerprint scanning, or device passcodes. This dynamic guarantees that even if a device is physically lost or stolen, unauthorized actors cannot execute transactions without the biometric consent of the legitimate owner.
Remote Management and Emergency Controls
In the unfortunate event that a physical wallet goes missing, the recovery process is tedious and stressful. Cardholders must contact individual issuers, cancel multiple cards, and wait days or weeks for replacements to arrive in the mail. Digital wallets invert this friction by integrating cloud-connected remote management tools into the user experience.
If a smartphone is misplaced, owners can immediately suspend or wipe their digital wallets remotely via cloud dashboards without canceling their actual underlying bank accounts. This instantaneous revocation window provides a crucial safety net that physical billfolds simply cannot match. Developers building these ecosystems prioritize instant state changes, ensuring that security directives propagate globally across payment networks in mere seconds.
The Developer Perspective: Building Secure FinTech Integrations
For software engineers and product teams building modern applications, integrating with digital wallets offers a streamlined path to robust security compliance. Instead of handling raw cardholder data—which triggers stringent Payment Card Industry Data Security Standard (PCI-DSS) auditing and enormous liability—developers can leverage native wallet APIs that handle tokenized payloads seamlessly.
This abstraction layer shifts the heavy lifting of compliance and cryptographic protection onto major platform providers and payment gateways. However, it also demands rigorous adherence to platform guidelines, secure API management, and careful handling of authentication flows. Developers must design applications that respect hardware boundaries and maintain the integrity of user authorization chains.
Remaining Vulnerabilities and New Threat Vectors
Despite their sophisticated defenses, digital wallets are not entirely immune to malicious activity. As hardware and tokenization security matures, cybercriminals have pivoted toward social engineering, phishing campaigns, and device-level malware designed to intercept one-time passcodes or manipulate user sessions. Attackers no longer target the transit layer; instead, they target the human element.
Additionally, issues surrounding device compromise, such as jailbroken or rooted hardware, can undermine the integrity of secure enclaves. Maintaining digital security requires ongoing vigilance, continuous firmware updates, and user education to ensure that the human link in the security chain remains as resilient as the underlying cryptography.
The Future of Secure Digital Transactions
The transition from physical currency and plastic cards to cryptographic digital wallets represents a milestone in financial technology. By combining tokenization, secure enclaves, biometrics, and instant cloud management, modern wallets offer a level of protection that legacy payment methods can never match. As digital ecosystems continue to expand, the principles governing digital wallet security will likely serve as the blueprint for securing broader identity and asset management systems.
Source: engadget.com