
Unsealed Records Reveal How Enterprise Analytics Tools Ingest Public Surveillance Data

The Blurring Boundary Between Enterprise Software and Mass Tracking
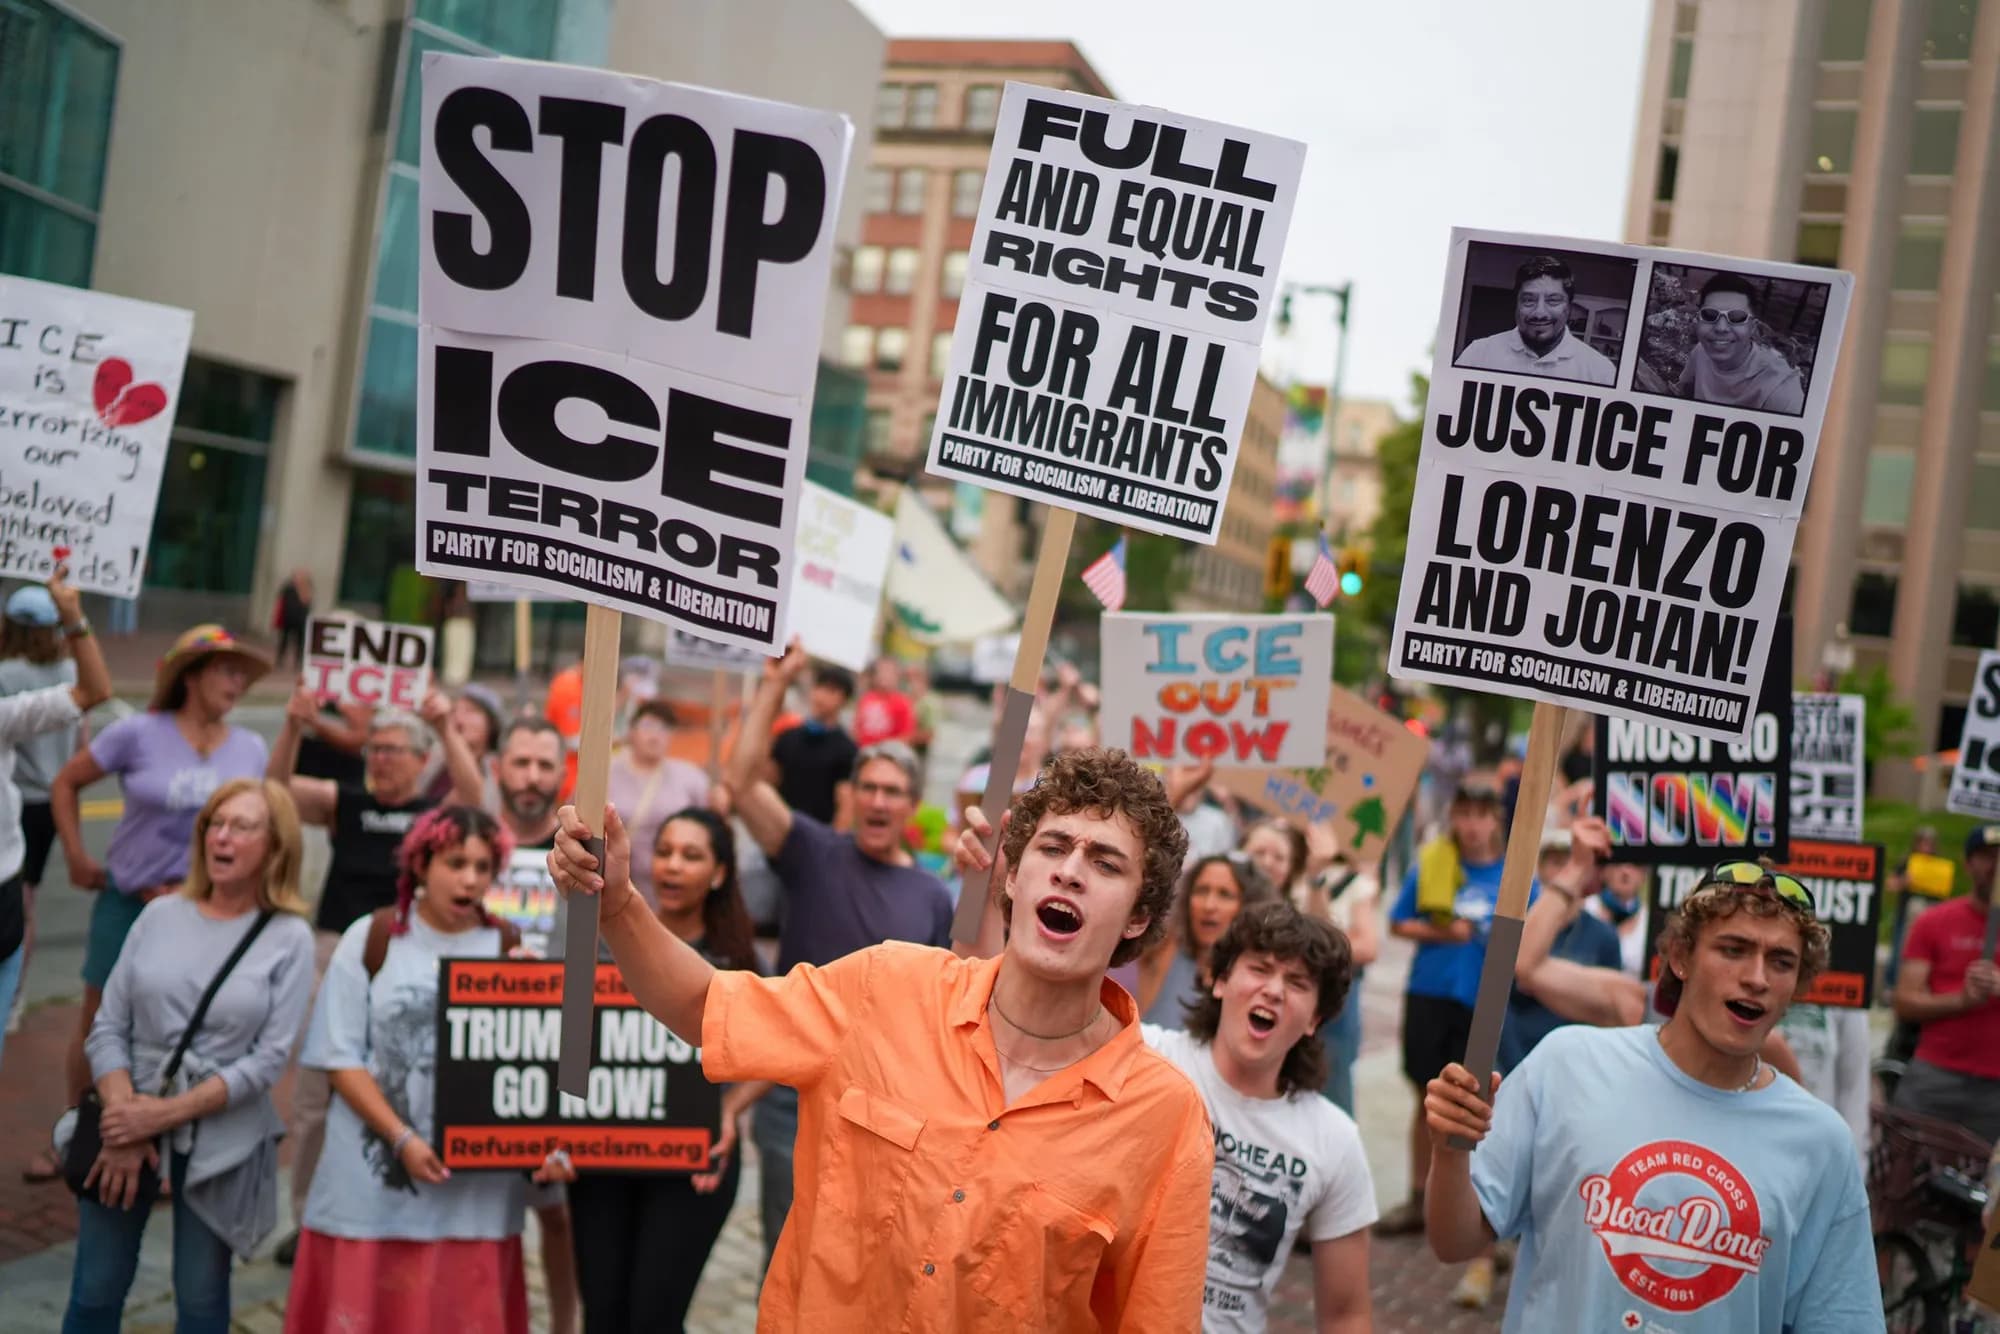
In modern software engineering, the lines between business intelligence, enterprise resource planning, and population-scale surveillance have grown vanishingly thin. Recent revelations originating from newly unsealed federal court filings have brought this reality back into sharp focus. According to these records, federal immigration enforcement officials systematically collected photographs and dossier information on community observers and activists monitoring enforcement activities in Maine, subsequently channeling those visual records directly into analytical databases provided by Palantir Technologies.
While civil liberties advocates have sounded alarms over the First and Fourth Amendment implications of documenting individuals exercising oversight of law enforcement, the technical mechanics of the practice deserve equal scrutiny. The case demonstrates how enterprise-grade ingestion pipelines and advanced graph-analytics platforms originally designed for counterterrorism and intelligence gathering have permeated regional, routine government operations. When everyday observations are converted into persistent database entries, the technical systems that house them shift from passive tools of record to active instruments of oversight.
Under the Hood: How Palantir Transforms Unstructured Field Data into Actionable Intelligence
Palantir has built its enterprise reputation on data unification platforms, primarily Gotham and Foundry, which specialize in integrating wildly disparate data streams into unified analytical environments. At an architectural level, these platforms do not function merely as relational tables or simple document stores. Instead, they operate atop sophisticated ontology layers and graph databases that map real-world entities—people, vehicles, phone numbers, geographic locations, and digital identifiers—to one another via explicit relationships.
When an enforcement agent uploads a field photograph into such a system, an automated ingestion pipeline kicks off. The unstructured file is assigned metadata, including device details, timestamps, and geolocation tags. From there, machine learning algorithms and computer vision models may extract facial vectors, optical character recognition (OCR) data from license plates or background signage, and spatial coordinates. Once ingested, the platform’s entity-resolution algorithms attempt to reconcile the new entity against existing nodes in the database, weaving an isolated snapshot into an expansive web of historical records, travel patterns, and interpersonal associates.
The Pipeline of Modern Surveillance: From Field Capture to Queryable Index
The workflow uncovered in recent court documents underscores how seamless field-to-cloud data movement has become for state actors. In legacy law enforcement contexts, photographic documentation often remained trapped inside local hard drives, digital camera memory cards, or paper incident reports. Querying those archives required manual labor, physical cross-referencing, and specific institutional memory.
In the current technological paradigm, however, field agents equipped with mobile applications or secure portals can stream media directly into central data repositories with negligible friction. Once an entry is indexed, any authorized operator across regional or national offices can query that data using natural language searches, image similarity lookups, or temporal-spatial bounding boxes. What once was an ephemeral observation on a public street corner is transformed into an immutable, searchable node within a distributed system, effectively lowering the cost and effort of continuous human tracking to nearly zero.
Engineering Ethics and the Dual-Use Dilemma in Software Design
For software developers, data architects, and security researchers, these disclosures emphasize the severe ethical responsibilities inherent in modern application development. Data platforms built for benign enterprise applications—such as supply-chain tracking, fraud prevention, or public transit optimization—frequently rely on the identical architectural patterns utilized in political monitoring and civil surveillance.
When engineers construct automated pipelines that ingest unstructured visual data without rigorous programmatic safeguards, the potential for mission creep becomes an architectural feature rather than a bug. Features like permissive access-control defaults, loose audit-logging requirements, and automated entity clustering can be weaponized against public oversight when deployed in governmental settings. Developers are increasingly confronted with the reality that software cannot be evaluated solely on its algorithmic efficiency; its operational intent and downstream human consequences are fundamentally intertwined with its technical implementation.
Data Retention, Cryptographic Auditing, and Policy Blind Spots
A primary technical failure highlighted by the unsealed filings is the systemic absence of lifecycle management for sensitive public data. In a well-architected cloud ecosystem, data retention policies enforce the automated deprecation, anonymization, or deletion of personal data when its retention lacks legal or operational justification. In surveillance deployments, however, ingestion pipelines often follow an append-only philosophy where data is hoarded indefinitely under the premise that it might possess analytical utility in the future.
To counteract such overreach, security engineers and technical ethicists frequently advocate for immutable, cryptographically verifiable audit logs. If an agency chooses to record citizens exercising constitutional rights, that data ingestion event should trigger immutable logging that is subject to third-party verification. Without cryptographic verification, automated data decay, and hard access-control barriers, surveillance databases inevitably expand unchecked, becoming institutional vaults of unvetted, potentially unconstitutional dossiers.
What Lies Ahead for Enterprise Data Vendors and Public Oversight
The integration of community observer photographs into Palantir databases marks another chapter in the growing intersection of private-sector software engineering and federal state power. Moving forward, both tech companies and the public sector will face mounting scrutiny over the procurement and deployment of enterprise analytics stacks. We are likely to see intensified pushback from privacy regulators, open-source software communities, and corporate whistleblowers demanding that software vendors implement technological guardrails against improper surveillance.
For the broader technology industry, this controversy serves as a stark reminder: code is not politically neutral. As computer vision, graph processing, and enterprise data consolidation continue to mature, the developers who design these systems must critically examine how their architectures function outside the laboratory. When the systems we build make tracking private citizens trivial, the responsibility to prevent systemic overreach rests not just with policy makers, but with the engineers architecting the underlying systems.
Source: wired.com